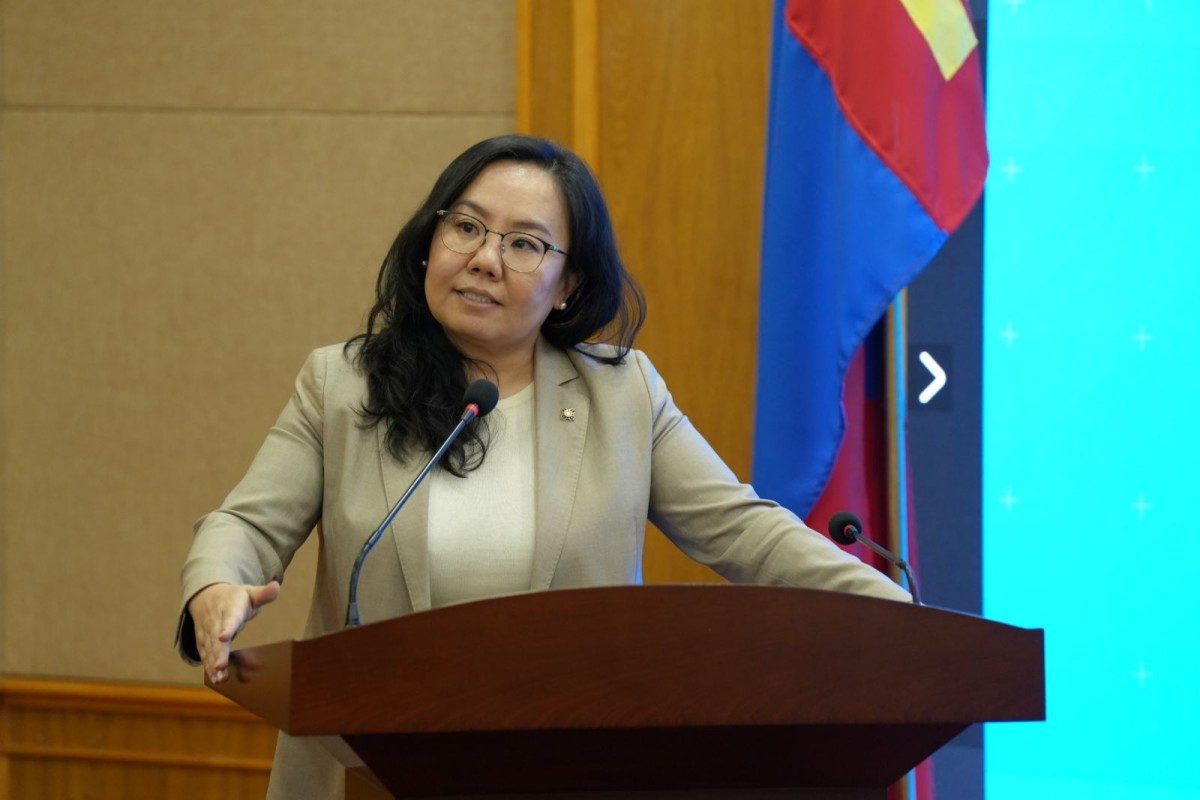
As non-banking financial institutions continue to broaden their activities, applying for loans and using online financial services have become routine for many people. At the same time, the wider availability of credit has led to frequent violations, including the misuse of citizens’ personal data without consent, repeated harassment of relatives under the guise of debt collection, and the continued storage of personal information even after loans are fully repaid. We discussed these issues with Dr.Narantuya Ganbat, Commissioner of the National Human Rights Commission of Mongolia.
- To begin with, could you explain what is meant by personal privacy and sensitive information? How are these defined in the law?
- Mongolia adopted the Law on the Protection of Personal Data in 2021, and it came into force on May 1, 2022. This law is distinctive because it comprehensively regulates the collection, processing, use, storage, and destruction of personal data in line with international standards. Before this, only a very general law with four provisions relating to personal privacy existed. The current law clearly defines key concepts, including personal data, sensitive data, and confidentiality. For instance, Subsection 4.1.12 specifies that information concerning ethnicity, religion, beliefs, health, correspondence, genetic and biometric data, digital signature private keys, criminal records and their execution, as well as sexual orientation, expression, and sexual relations, falls under sensitive information. Section 9.1 further categorizes certain types of data—such as health, correspondence, genetic and biometric data, digital signature keys, and information related to sexual orientation and expression as data subject to heightened confidentiality protections.
- Is Mongolia currently able to enforce this law effectively?
- Under the law, the NHRCM submits an annual “Report on the Status of Human Rights and Freedoms in Mongolia” to parliament. In March 2025, the report included an assessment of how the personal data protection law is being implemented, particularly in relation to digital technology and human rights. Today, personal data is often described as the oil of the digital era. Information about people’s behavior, lifestyles, and consumption patterns has significant economic value, as it can be used to determine which goods and services are offered to whom, and even to influence individuals’ social and political decisions. For this reason, protecting personal data has become a core human rights issue.
- How would you assess citizens’ awareness toward protecting their personal information?
- Many people in Mongolia still do not fully understand that safeguarding personal data is essential to protecting their privacy. For example, if someone on the street is asked, “We have a promotion, please share your registration number,” how many would refuse? This illustrates the low level of awareness around personal data protection. During the domestic spread of COVID-19, citizens’ names, registration numbers, and phone numbers were publicly disclosed without any safeguards under the guise of contact tracing. Such violations were even acknowledged during State Emergency Commission press briefings, highlighting how weak public understanding and attitudes toward information privacy remain.
Legally, personal data should only be collected for clearly defined purposes, with the consent of the data subject, or by authorized bodies acting within their legal mandate. In practice, however, these requirements are often ignored, and more data than necessary is routinely collected. Although Mongolia’s law is inspired by the EU’s General Data Protection Regulation, the key principle of data minimization is not sufficiently reflected in its implementation.
In recent years, cyberattacks and negligence by data controllers have also led to widespread leaks of citizens’ personal information. When electronically collected data is shared, strong encryption and security measures should be used to ensure confidentiality. Due to the absence or weakness of such safeguards, large volumes of personal data have been lost, either deliberately or unintentionally. Furthermore, government agencies sometimes publicly disclose information about the handling of applications, complaints, or even patients’ medical histories in paper form, which constitutes a clear violation of personal data protection laws.
A mobile phone number is also personal data. Yet citizens complain that non-banking financial institutions contact their family members, relatives, and workplaces even when a loan is only slightly overdue.
There is a fundamental principle that personal information may only be used for the purpose for which it was originally collected. Naturally, if a borrower fails to meet their contractual obligations, the lender has the right to take lawful steps to ensure repayment. However, this process must begin by contacting the borrower directly and resolving the matter in accordance with the law. Calling siblings or relatives, or publishing a person’s personal details on social media under the pretext of debt collection, constitutes a serious misuse of personal data for purposes beyond those originally agreed upon. That said, in some cases it may be necessary to collect limited information about related persons, such as for loan guarantees. Even then, collecting the phone numbers of ten acquaintances or requesting their Facebook accounts clearly violates the principle of collecting the minimum amount of data. This is why both the method of data collection and the purpose for which it is used are critically important. Some organizations, including those operating under names such as “Sain International” and “Tus Fintech,” are accused of harassing citizens by shouting and making repeated calls day and night. Given Mongolia’s current economic and financial conditions, very few people do not rely on loan applications. According to the Financial Regulatory Commission’s Personal Data Protection Unit, around 50 loan applications registered with the commission are actively operating, while approximately 30 more are under development. It is estimated that about 1.3 million citizens receive some form of loan through these platforms. The Financial Regulatory Commission has previously reviewed and resolved numerous concrete cases of personal data violations involving the organizations mentioned.
- Roughly how many complaints related to personal data breaches by non-bank financial institutions has the NHRCM received this year?
- In total, the commission received 31 complaints and reports concerning breaches or disclosures of personal information, three of which involved non-bank financial institutions. By law, organizations are required to submit annual records of personal data violations to the commission by January 31. This year, the commission issued specific guidelines for private-sector regulators and licensing bodies overseeing organizations that handle large volumes of sensitive personal data. Under these guidelines, sector regulators will gather violation records from businesses in their fields and submit them to the commission within the legally prescribed timeframe.
There is a fundamental principle that personal information may only be used for the purpose for which it was originally collected. Naturally, if a borrower fails to meet their contractual obligations, the lender has the right to take lawful steps to ensure repayment. However, this process must begin by contacting the borrower directly and resolving the matter in accordance with the law.
- Shouldn’t personal information be deleted once a loan has been fully repaid?
- Article 15 of the Law on the Protection of Personal Information clearly sets out the grounds for deleting personal data. In addition, unless otherwise specified by law, information must be erased immediately once the original purpose for its collection has been fulfilled, the contractual period has ended, or the parties have reached a mutual agreement. Credit databases should contain information only on non-performing loans; citizens who have met their contractual obligations fully and on time should not be included. Banks and financial institutions do have the right, within the law, to retain loan disbursement and repayment records for a certain period in order to meet obligations such as accounting and reporting. However, once such information is no longer necessary, the principle of prompt deletion must apply. For this reason, the Financial Regulatory Commission needs to clearly define what types of data may be retained and the specific duration for which they can be lawfully stored.
- What advice would you give citizens if their personal information is lost or misused? Where should they turn first?
- When the Law on the Protection of Personal Information is violated, there are four legal frameworks and five mechanisms through which citizens’ rights can be restored. The Criminal Code and the Infringement Law play a central role in this process. If a complaint or report received by the NHRCM involves a potential crime, action is taken under criminal law; if it constitutes an offense, it is handled under the Infringement Law. In both cases, the commission forwards the matter to the police for investigation. For other types of complaints, the commission conducts its own review, determines whether a human rights violation has occurred, and resolves the issue by issuing demands or recommendations. If it is confirmed that an organization, official, or legal entity has violated human rights and freedoms, a formal demand is submitted requiring the violation to be remedied. If there is a risk that a violation may occur, the commission issues recommendations aimed at eliminating the underlying causes and conditions. Entities that receive these demands or recommendations are legally obligated to comply. In addition, the Civil Service Law and the Labor Law also serve as mechanisms for restoring rights. If a personal data violation does not amount to a crime or offense, the organization may still impose disciplinary or other internal accountability measures against the responsible individual.
- Does the current legal framework realistically protect citizens’ data rights?
- At present, criminal and offense-related legislation does not fully meet the needs of modern personal data protection. The definitions of crimes and offenses have not been sufficiently updated to align with the spirit and scope of the new law. While provisions in the Criminal Code such as those addressing unauthorized photography or recording, invasion and disclosure of privacy, illegal surveillance, and the spread of false information are intended to protect personal data, they do not adequately correspond to the realities addressed by the current data protection law. A new provision has been added to the Infringement Law that recognizes acts such as using personal data without consent, using data for purposes other than those originally stated, processing data through artificial intelligence without human oversight in ways that harm human rights, and illegally obtaining or transmitting sensitive data. Although these are positive steps, the associated fines remain extremely low. Once personal data is exposed, the harm caused is often irreversible. There is also a lack of clarity regarding the liability of data controllers who deliberately ignore lawful requests from data subjects. For instance, when data breaches occur due to cyberattacks, private organizations often attempt to conceal the incident to protect their reputation. In such cases, accountability mechanisms remain vague. As a result, citizens’ personal data protection remains weak overall. Fundamentally, Mongolia needs to establish a single, clearly defined authority responsible for data protection. In many countries, there are dedicated state inspectorates for personal data with the power to impose substantial fines. Mongolia does not yet have such an institution. The commission member’s demands are designed to prompt action by authorized officials, not to directly penalize organizations. While action can be taken through the police under the Infringement Law, the fines imposed are insignificant compared to the true value of personal data, which undermines effective legal protection.
- For example, how large are these fines in practice?
- Legally, fines range from two to 20 million MNT. In reality, however, penalties of only 1 million to 2.5 million MNT are typically imposed. To date, no organization in Mongolia has been fined the maximum amount. In major data breach cases involving institutions such as Khaan Bank and Intermed Hospital, the fines applied were clearly insufficient given the scale of the violations. Personal data will only continue to grow in value. As artificial intelligence advances and technologies capable of processing vast amounts of information become more widespread, the need to strengthen legal protections for personal information will become increasingly urgent. Mongolia must establish a robust personal data protection authority capable of monitoring and sanctioning serious violations. At the same time, it is essential to build a unified cybersecurity framework bringing together institutions such as the police, the Communications Regulatory Commission, and the State Digital Services Regulatory Agency to quickly identify breaches and ensure accountability.
By M.IVEEL